Security and governance in Oracle AI Data Platform
Oracle AI Data Platform brings security, access control, catalog-based governance, lineage, and auditability into the same environment used to build and run data, analytics, models, and agents. Customers define identities, roles, policies, and permissions. The platform then applies those controls across managed and catalogued assets—governing data access, collaboration, and AI execution.
Why choose Oracle AI Data Platform for data security, governance?
-
You control access and governance
Use Oracle Cloud Infrastructure Identity and Access Management for identity and authentication and AI Data Platform role-based access control for fine-grained permissions inside the platform. You define who can access, administer, discover, use, or change platform resources.
-
Govern data and AI together
Apply access permissions across data and AI assets and workspaces—including catalogs, tables, columns, models, knowledge bases, and agents—supported by governance metadata, lineage, and lifecycle controls.
-
Collaborate without losing control
Keep workspace collaboration separate from data permissions, so users can find and access only the assets they’re authorized to use, while governed data can be shared with specific authorized recipients without creating unnecessary copies.
Explore security and governance across AI Data Platform
Security and governance run across the platform rather than sitting in one product feature. Oracle AI Data Platform combines Oracle Cloud Infrastructure Identity and Access Management, platform role-based access control, private networking, catalog governance, lineage, registries, observability, and audit logs. You retain authority over policies and execution boundaries; the platform applies those controls to workspaces and assets under its management.
Control identity and access
Two-layer security model
Use Oracle Cloud Infrastructure Identity and Access Management for identity, authentication, and cloud-level access, with AI Data Platform role-based access control for fine-grained authorization inside the platform.
Fine-grained roles and permissions
Control access across workspaces, catalogs, schemas, tables, volumes, compute, agents, tools, and administrative functions according to each user's or workload's responsibilities.
Permission-aware discovery
Users and AI workloads can discover and use only the assets they are authorized to access. Collaborating in a workspace does not automatically grant access to all underlying data.
Protect data and workloads
Private network isolation
Deploy supported workspaces, compute, and data connections through private VCN subnets and private endpoints so sensitive workloads can remain off the public internet.
Credential and connection protection
Use integrated secrets, credential, certificate, and TLS controls—including Oracle Cloud Infrastructure Vault and Oracle Cloud Infrastructure Certificates—to help protect access to data, services, and external connections.
Controlled sharing and access in place
Share data through supported paths without unnecessary duplication while keeping recipient access explicit, scoped, and auditable. In-place access depends on the source and integration path.
Govern data and AI assets
Unified catalog and ownership
Organize data and AI assets—including tables, files, volumes, knowledge bases, models, feature stores, and agent definitions—with consistent metadata, ownership, and access policies.
End-to-end lineage and lifecycle
Trace your data from source to consumption. Track supported assets down to individual columns as they move through transformations into downstream data products, AI/ML models, and AI applications. See where data originated, how it changed, and which downstream assets a change could affect.
Registration and reuse
Register approved ML models and experiments, agents, and reusable agent tools, including MCP, SQL, and RAG tools. Capture version history, permissions, lineage, and descriptive metadata for ML models and experiments, while cataloging approved agents and tools so teams can discover and reuse them with the appropriate controls.
Make AI accountable
Audit logging and traceability
Record user activity, data access, agent interactions, and administrative changes to support compliance, investigation, and access-history reporting.
Agent observability
Inspect agent runs, tool calls, inputs, outputs, status, duration, errors, latency, token usage, and other operational signals across development and production.
Human authority and bounded action
Keep AI agents and workflows inside customer-defined permissions, policies, approvals, checkpoints, and execution boundaries. People retain authority over outcomes and consequential decisions.
See AI Data Platform security and governance in action
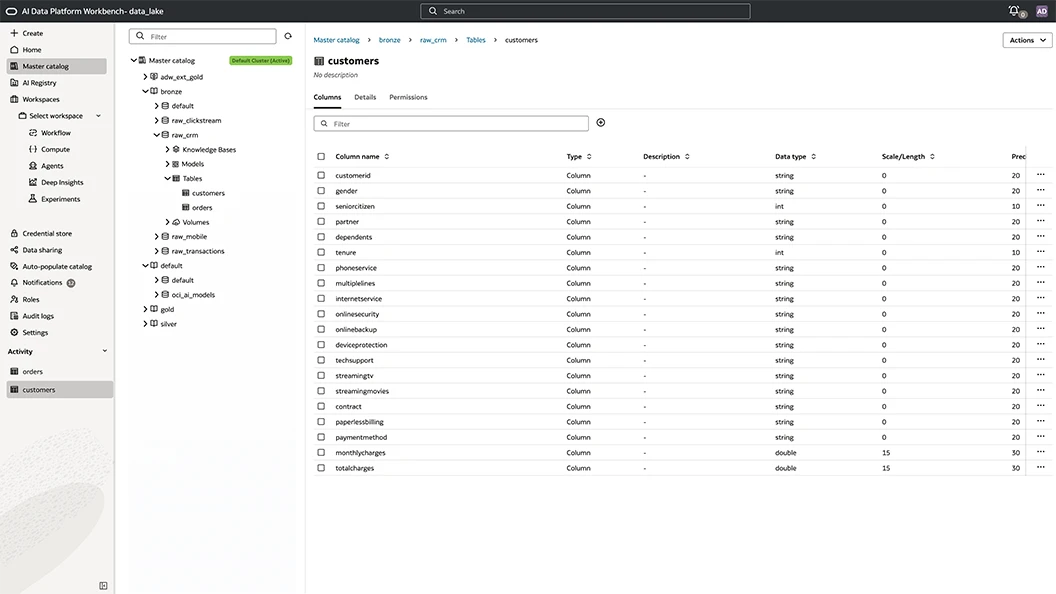
A unified metadata layer across your entire Oracle Cloud data estate
The master catalog helps teams discover and understand enterprise data by organizing metadata—asset names, locations, schemas, column definitions, and file formats—into a unified inventory. It connects to structured assets, such as tables and views, alongside unstructured content across Autonomous AI Database, Oracle Database, Oracle Cloud Infrastructure Object Storage, and third-party data lakes, without moving or copying the underlying data.
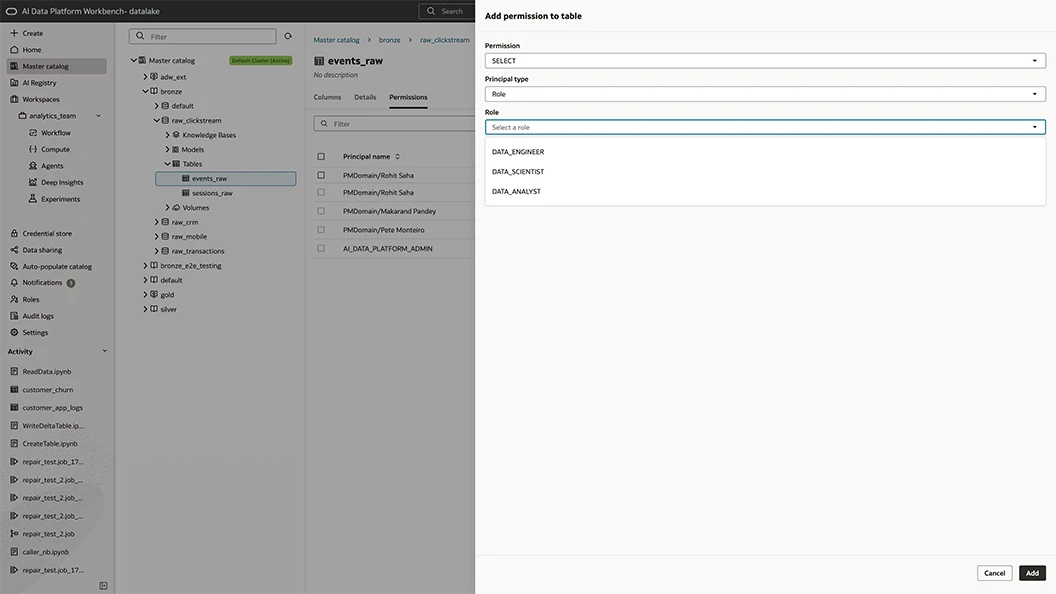
Consistent access control across all AI and data workloads
A centralized, role-based access management framework supports secure data usage. Oracle AI Data Platform provides fine-grained access controls and policy management at the data layer, helping you manage how users and AI workloads access data while supporting scalable AI initiatives.
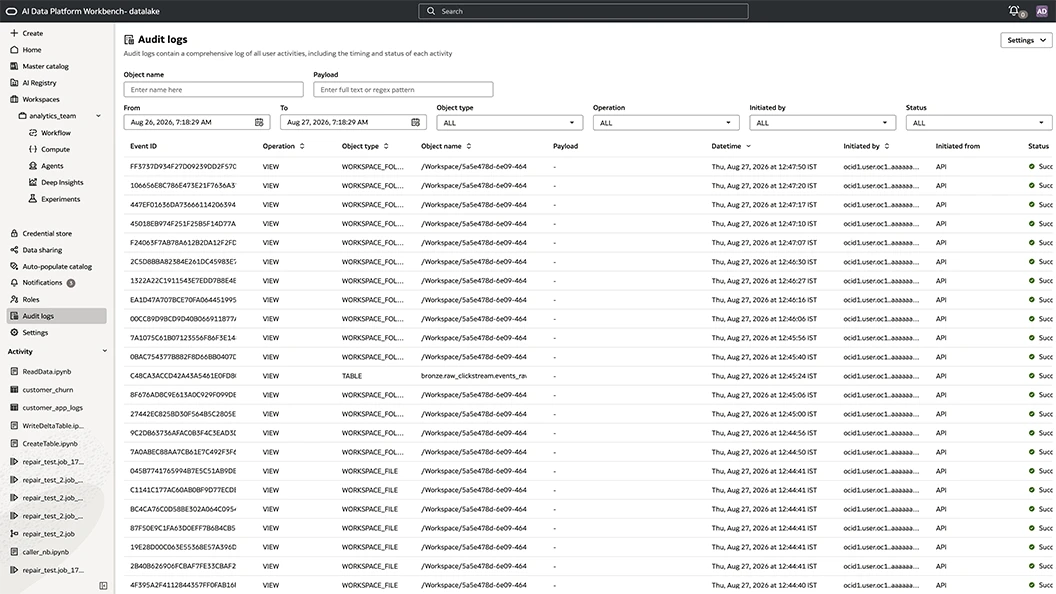
Complete visibility into data access across all AI and data workloads
Provide transparency and security with audit logs that track who accessed what data, when, and how. Gain end-to-end visibility across Oracle AI Data Platform for auditing and operational oversight.
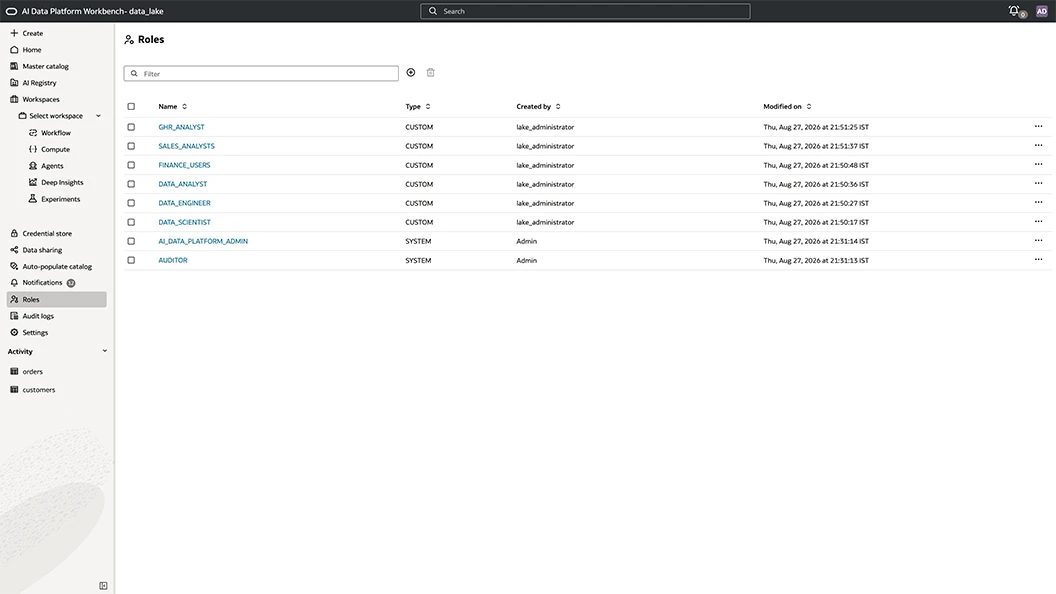
Role-based access management across AI and data workloads
Define and manage roles across Oracle AI Data Platform so that users and AI workloads have appropriate access to data, tools, and platform resources. Granular role-based controls help simplify administration, strengthen security, and make it easier to apply access policies.
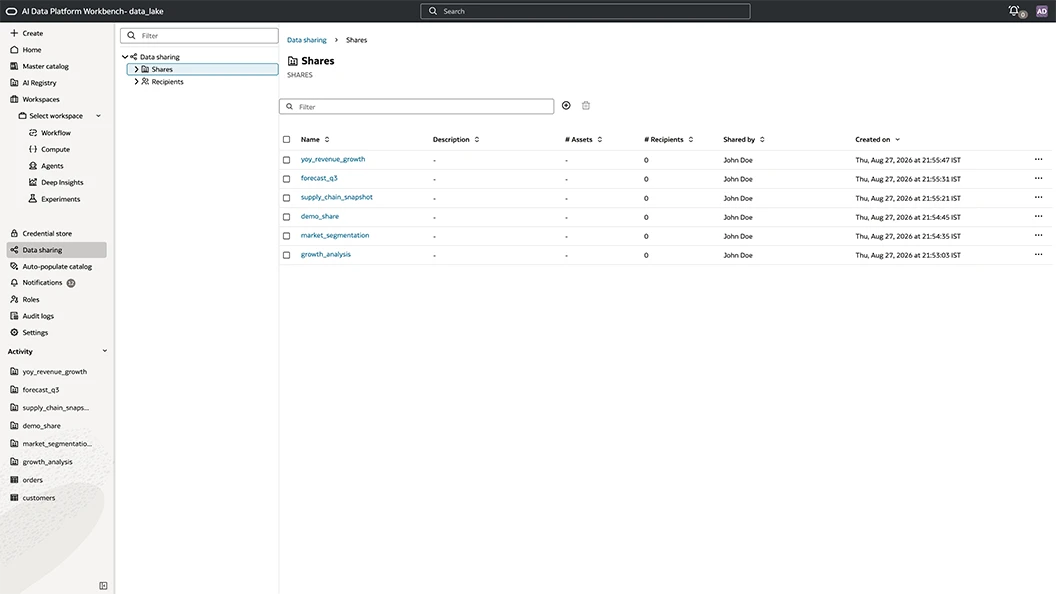
Seamless data sharing
Securely share data across teams and projects without unnecessary duplication or data movement. Oracle AI Data Platform enables controlled, policy-driven data sharing that helps improve collaboration, accelerate access to trusted data, and simplify enterprise-scale data operations.
추천 AI Data Platform 블로그
에이전트 vs. 워크플로: ROI는 실제로 어디에서 발생할까요?
대부분의 기업이 AI 에이전트 도입에 실패하는 이유는 기술 때문이 아니라, 단순한 워크플로로 더 잘 처리할 수 있는 업무에 에이전트를 사용하고 있기 때문입니다. 이 블로그에서는 워크플로와 자율형 에이전트의 주요 차이점과, 올바른 접근 방식을 선택하는 것이 ROI, 확장성, 거버넌스 및 비용에 어떤 영향을 미치는지 설명합니다. 또한 에이전틱 AI가 실제로 투자할 가치가 있는지 판단할 수 있는 실용적인 프레임워크를 제공합니다.
-
2026년 5월 12일
인프라 엔지니어로 계약하신 건 아니잖아요
-
2026년 2월 13일
Enterprise AI의 3가지 구성 요소
-
2025년 12월 8일
Oracle AI Data Platform 여정 시작하기